Rate this post

Download Microsoft SC-300 Mock Test Study Material

SC-300 Questions Prepare with Learning Information

QUESTION 44
You have 2,500 users who are assigned Microsoft Office 365 Enterprise E3 licenses. The licenses are assigned to individual users.
From the Groups blade in the Azure Active Directory admin center, you assign Microsoft 365 Enterprise E5 licenses to the users.
You need to remove the Office 365 Enterprise E3 licenses from the users by using the least amount of administrative effort.
What should you use?


QUESTION 45
You have a Microsoft 365 tenant.
All users have mobile phones and laptops.
The users frequently work from remote locations that do not have Wi-Fi access or mobile phone connectivity.
While working from the remote locations, the users connect their laptop to a wired network that has internet access.
You plan to implement multi-factor authentication (MFA).
Which MFA authentication method can the users use from the remote location?


QUESTION 46
You have an Azure Active Directory (Azure AD) tenant that contains a user named User1 and the groups shown in the following table.

In the tenant, you create the groups shown in the following table.

Which members can you add to GroupA and GroupB? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 47
You have a Microsoft 365 tenant.
You configure a conditional access policy as shown in the Conditional Access policy exhibit. (Click the Conditional Access policy tab.)

You view the User administrator role settings as shown in the Role setting details exhibit. (Click the Role setting details tab.)

You view the User administrator role assignments as shown in the Rote assignments exhibit. (Click the Role assignments lab.)

For each of the following statement, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 48
You have an Azure subscription that contains the users shown in the following table.

You need to implement Azure AD Privileged Identity Management (PIM).
Which users can use PIM to activate their role permissions?


QUESTION 49
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. as a result, these questions will not appear in the review screen.
You have an Amazon Web Services (AWS) account a Google Workspace subscription, and a GitHub account You deploy an Azure subscription and enable Microsoft 365 Defender.
You need to ensure that you can monitor OAuth authentication requests by using Microsoft Defender for Cloud Apps.
Solution: From the Microsoft 365 Defender portal, you add the GitHub app connector Does this meet the goal?


QUESTION 50
You have an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.

For which users can you configure the Job title property and the Usage location property in Azure AD? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 51
You have an Azure AD tenant that contains the users shown in the following table.

You have the Azure AD Identity Protection policies shown in the following table.

You review the Risky users report and the Risky sign-ins report and perform actions for each user as shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 52
You have a new Microsoft 365 tenant that uses a domain name of contoso.onmicrosoft.com.
You register the name contoso.com with a domain registrar.
You need to use contoso.com as the default domain name for new Microsoft 365 users.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

QUESTION 53
You need to meet the technical requirements for the probability that user identifies were compromised.
What should the users do first, and what should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 54
You have a Microsoft 365 E5 subscription.
You need to create a dynamic user group that will include all the users that do NOT have a department defined in their user profile.
How should you complete the membership rule? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 55
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint Online site named Site!. Site!
hosts PDF files
You need to prevent users from printing the files directly from Sitel.
Which type of policy should you create in the Microsoft Defender for Cloud Apps portal?


QUESTION 56
You have an Azure AD tenant that contains the users shown in the following table.

You have the Azure AD Identity Protection policies shown in the following table.

You review the Risky users report and the Risky sign-ins report and perform actions for each user as shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 57
Your network contains an on-premises Active Directory Domain services (AD DS) domain that syncs with an Azure AD tenant. The AD DS domain contains the organizational units (OUs) shown in the following table.

You need to create a break-glass account named BreakGlass.
Where should you create BreakGlass, and which role should you assign to BreakGlass? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 58
You have a hybrid Microsoft 365 subscription that contains the users show in the following table.

You plan to deploy an on-premises app1. App1 will be registered in Azure AD and will use Azure AD Application Proxy.
You need to delegate the installation of the Application Proxy connector and ensure that User1 can register App1 in Azure AD. The solution must use the principle of least privilege.
Which user should perform the installation, and which role should you assign to Users1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 59
You have an Azure Active Directory (Azure AD) tenant that contains the following group:
Name: Group1
Members: User1, User2
Owner: User3
On January 15, 2021, you create an access review as shown in the exhibit. (Click the Exhibit tab.)

Users answer the Review1 question as shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 60
You have a Microsoft 36S tenant.
You create a named location named HighRiskCountries that contains a list of high-risk countries.
You need to limit the amount of time a user can stay authenticated when connecting from a high-risk country.
What should you configure in a conditional access policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 61
You have an on-premises Microsoft Exchange organization that uses an SMTP address space of contoso.com.
You discover that users use their email address for self-service sign-up to Microsoft 365 services.
You need to gain global administrator privileges to the Azure Active Directory (Azure AD) tenant that contains the self-signed users.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

QUESTION 62
You have a Microsoft 365 tenant.
You configure a conditional access policy as shown in the Conditional Access policy exhibit. (Click the Conditional Access policy tab.)

You view the User administrator role settings as shown in the Role setting details exhibit. (Click the Role setting details tab.)

You view the User administrator role assignments as shown in the Role assignments exhibit. (Click the Role assignments lab.)

For each of the following statement, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 63
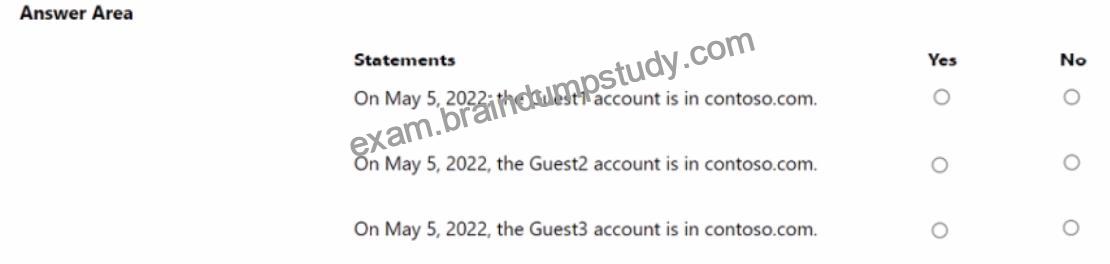
You have an Azure AD tenant named contoso.com that contains a group named All Company and has the following Identity Governance settings:
* Block external users from signing in to this directory: Yes
* Remove external user Yes
* Number of days before removing external user from this directory: 30
On March 1, 2022, you create an access package named Package1 that has the following settings:
* Resource roles
o Name: All Company
o Type: Group and Team
o Role: Member
* Lifecycle
o Access package assignment expire: On date
o Assignment expiration date: April 1, 2022
On March 1, 2022, you assign Package1 to the guest users shown in the following table.
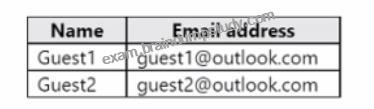
On March 2, 2022, you assign the Reports reader role to Guest1.
On April 1(2022, you invite a guest user named Guest3 to contoso.com.
On April 4, 2022, you add Guest3 to the All Company group.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
QUESTION 64
You have an Azure Active Directory (Azure AD) tenant that contains three users named User1, User1, and User3, You create a group named Group1. You add User2 and User3 to Group1.
You configure a role in Azure AD Privileged identity Management (PIM) as shown in the application administrator exhibit. (Click the application Administrator tab.)

Group1 is configured as the approver for the application administrator role.
You configure User2to be eligible for the application administrator role.
For User1, you add an assignment to the Application administrator role as shown in the Assignment exhibit.
(Click Assignment tab)

For each of the following statement, select Yes if the statement is true, Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 65
You have a Microsoft 365 E5 subscription that contains three users named User1, User2, and User3.
You need to configure the users as shown in the following table.

Which portal should you use to configure each user? To answer, drag the appropriate portals to the correct users. Each portal may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

QUESTION 66
You need to meet the technical requirements for the probability that user identifies were compromised.
What should the users do first, and what should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.


Most Reliable Microsoft SC-300 Training Materials: https://www.braindumpstudy.com/SC-300_braindumps.html


Related Links: myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt www.stes.tyc.edu.tw myportal.utt.edu.tt myportal.utt.edu.tt